A connector is just a tool Okou can pick up and use on your behalf. Slack, Notion, Gmail, GitHub, Linear, Stripe — once you connect one, Okou stops talking about your work and starts doing it.
Say you ask Okou, "Draft the launch announcement in Notion and drop the link in #marketing." With Notion and Slack connected, that isn't a hypothetical anymore. Okou opens Notion, creates the page, writes the draft, then posts it to Slack — the same way you would, just faster.
How connecting works
Okou can request a connector while it is working, or you can open Connectors from the workspace and set it up first. Two separate decisions are involved:
- Connect links or enables the current member's account for that service. OAuth and manually entered credentials belong to that member unless the connector explicitly says otherwise.
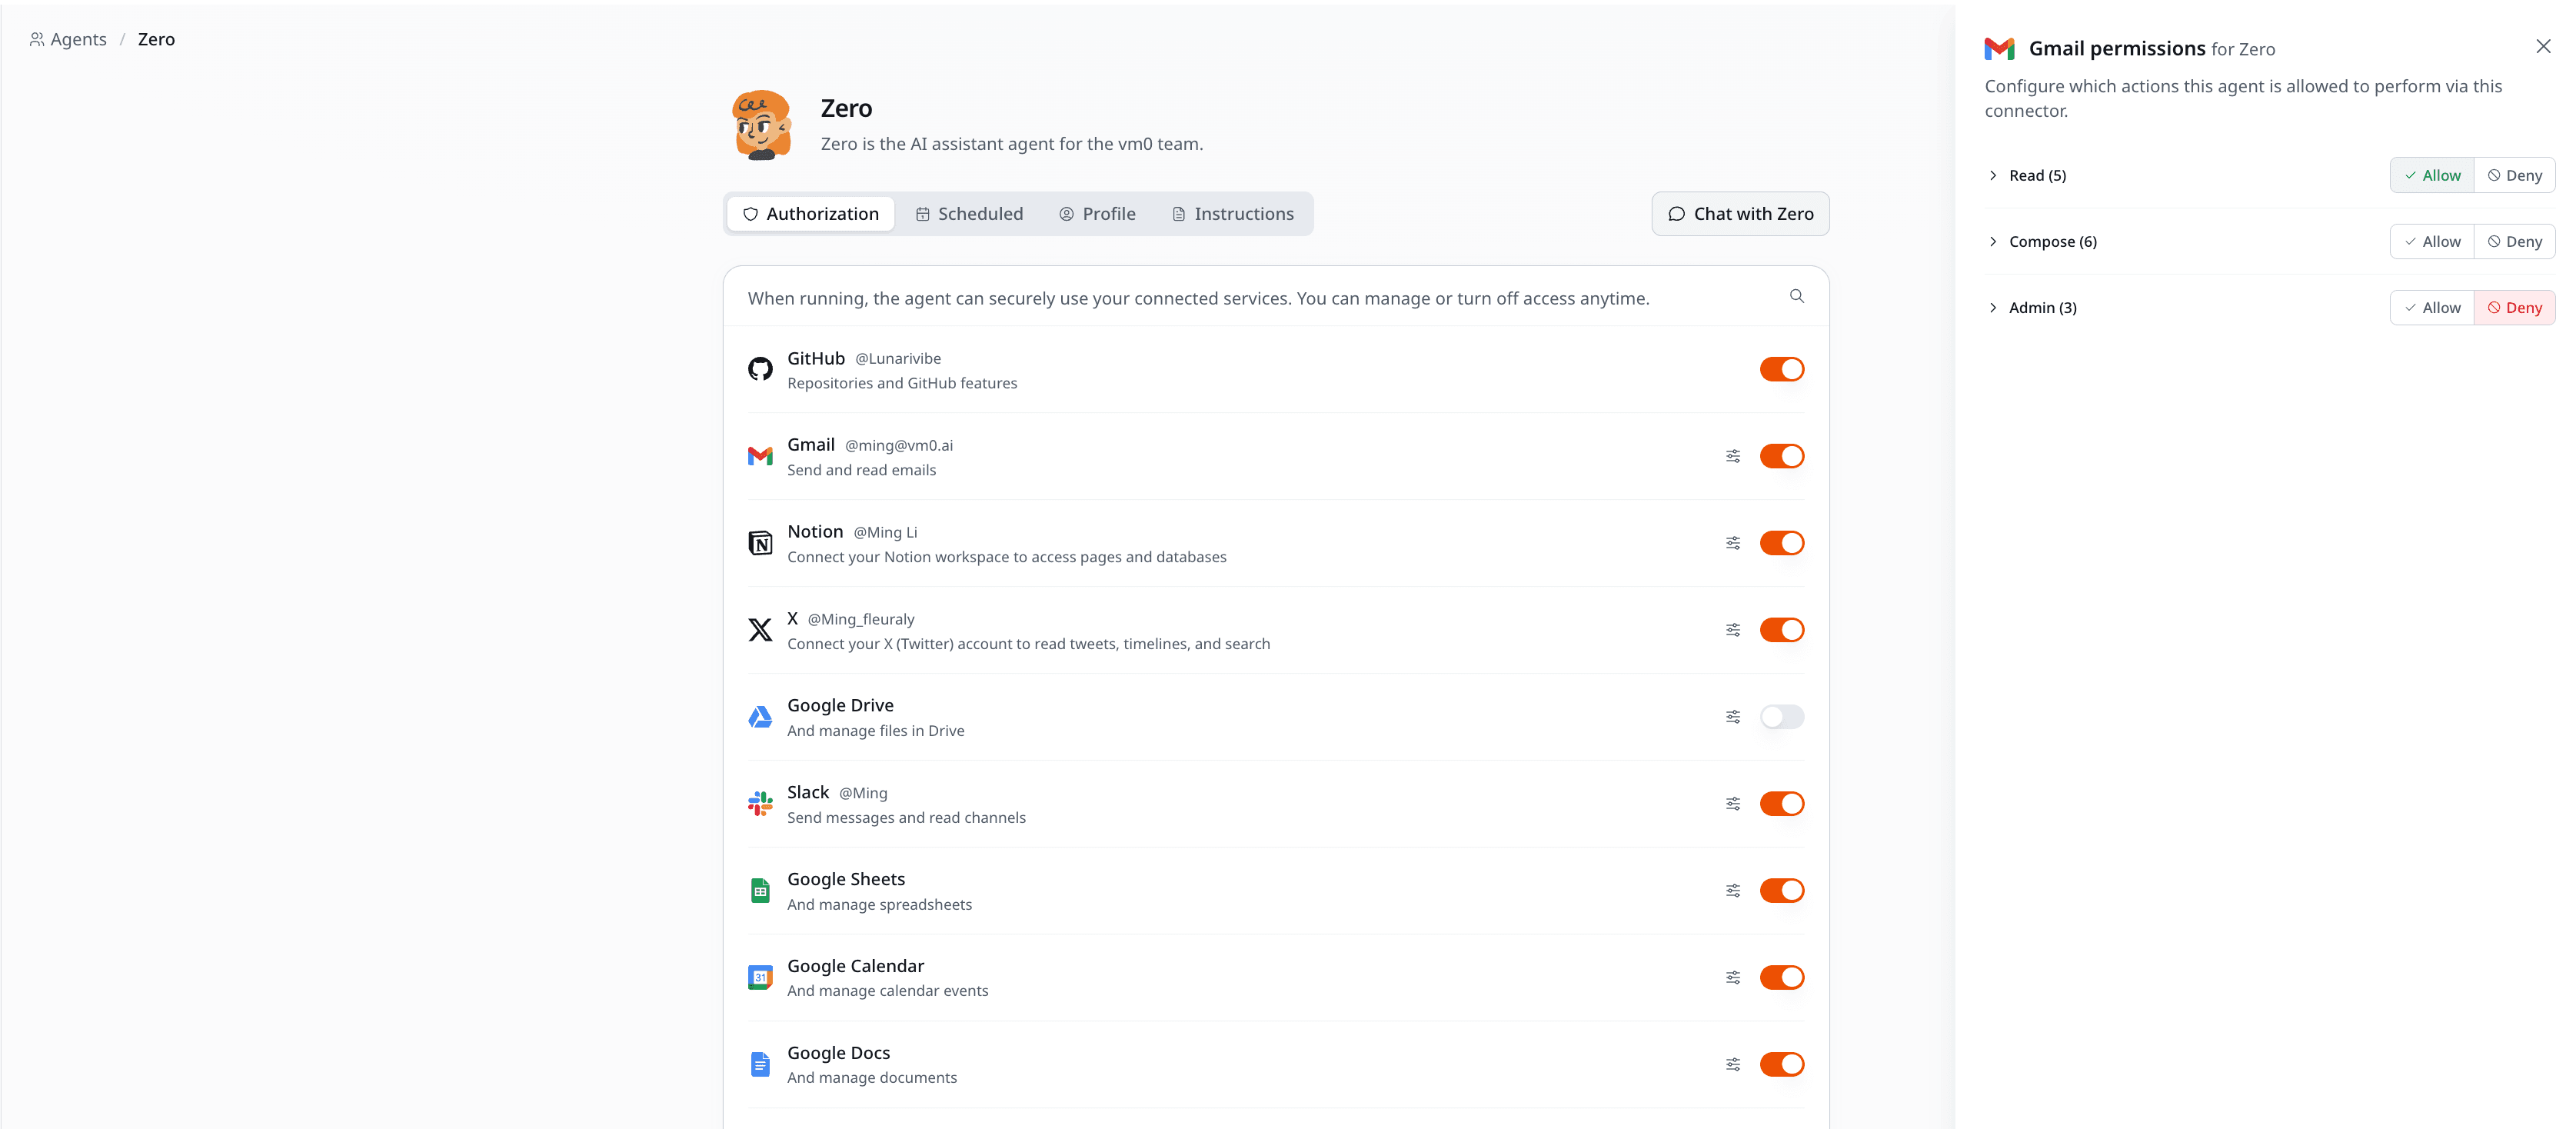
- Authorize and grant permissions controls whether Okou can use the connection and which named actions are allowed. In My Okou, follow the account and permission flow shown; no specialist Agent selection is required. In Legacy Agents, authorize the Agent that needs the connection. A connection does not grant every action.
An inline card can guide you through both steps. After the connection finishes, review the requested actions and choose an access duration. Okou can then continue the task within that access.
Do not assume a teammate's connection gives you access to their account. Each member connects their own account where the service uses per-member credentials.
First connection checklist
- Open Connectors, use Discover, and search for the service (older interfaces may use Built-in).
- Select Connect and finish the provider's sign-in or credential flow.
- My Okou: review the intended account. Legacy Agents: choose the Agent that needs the connector.
- Review its requested permissions and choose Allow for 1h, Allow for 24h, Allow for 7d, or Allow always as appropriate.
- Return to the original chat and retry only if the run did not resume.
If the account is connected but a task is still blocked, check the applicable account access, authorization, and specific denied permission. Connection status alone is not proof that the requested action is allowed.
A taste of what Okou can do
A few examples of how connectors translate into actual work:
- Notion — create pages, update databases, file meeting notes, draft proposals, search across your workspace.
- Slack — send DMs, post to channels, summarize long threads, follow up on stale conversations.
- Gmail — read your inbox, surface what actually needs your attention today, and prepare replies as drafts in your account. Okou writes the draft; you press send.
- GitHub — open issues, comment on PRs, triage the backlog, draft release notes.
- Linear — file tickets, move tasks across statuses, generate sprint summaries.
- Stripe, HubSpot, Calendar, Drive, Sheets, Docs… — same idea, in whichever tool the work lives.
You never have to explain how a tool works. Okou already knows. You describe the outcome; it handles the clicks.
You choose what Okou can do
Authorizing a tool isn't all-or-nothing. For every connector, you pick which actions Okou is allowed to take — and you can tighten or loosen those choices any time from Connectors; in Legacy Agents, also use the Agent's Authorization settings.
Legacy Agents example: